Gravwell Resources
Learn about everything from customer success stories, product info, to viewpoints from
the core team.
Blog
Not everyone is comfortable handing over the keys to their cybersecurity program to agents, and one reason is that many SIEM AI capabilities are still surface-deep. They draw conclusions solely from limited, preassembled context such as alerts, cases, and preconfigured integrations.
All
Exploring Absurdity: Windows Event Logs and Binary Logs
How to move to Gravwell from Splunk (or another platform)
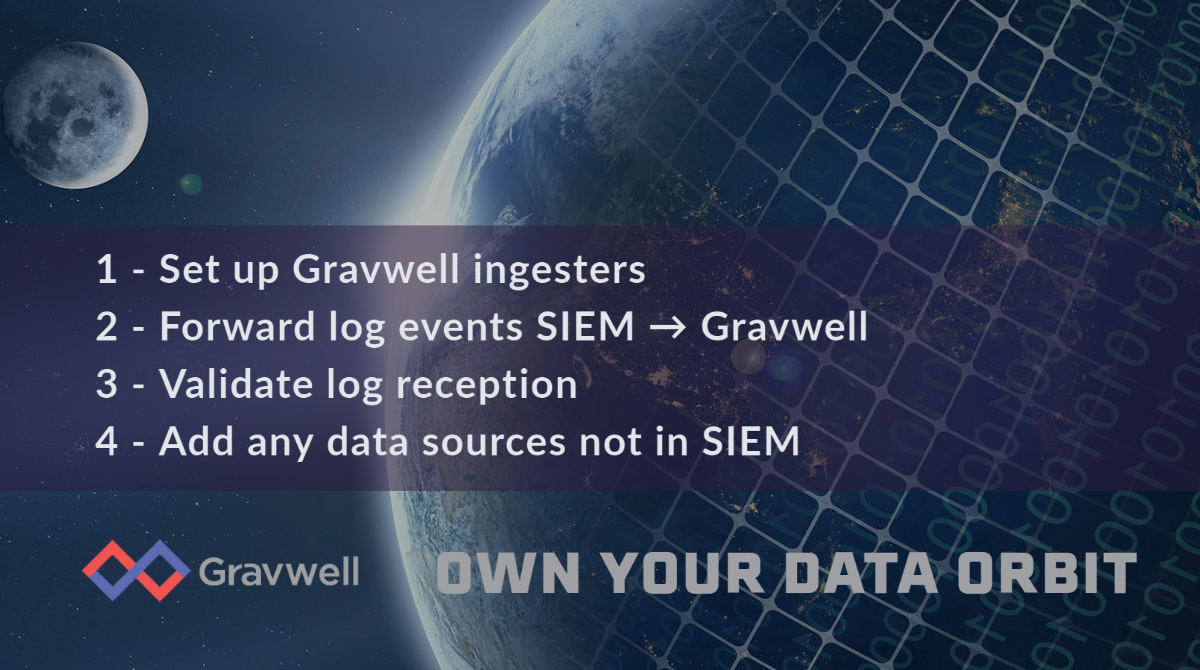
Add Threat Hunting to your SIEM with Gravwell
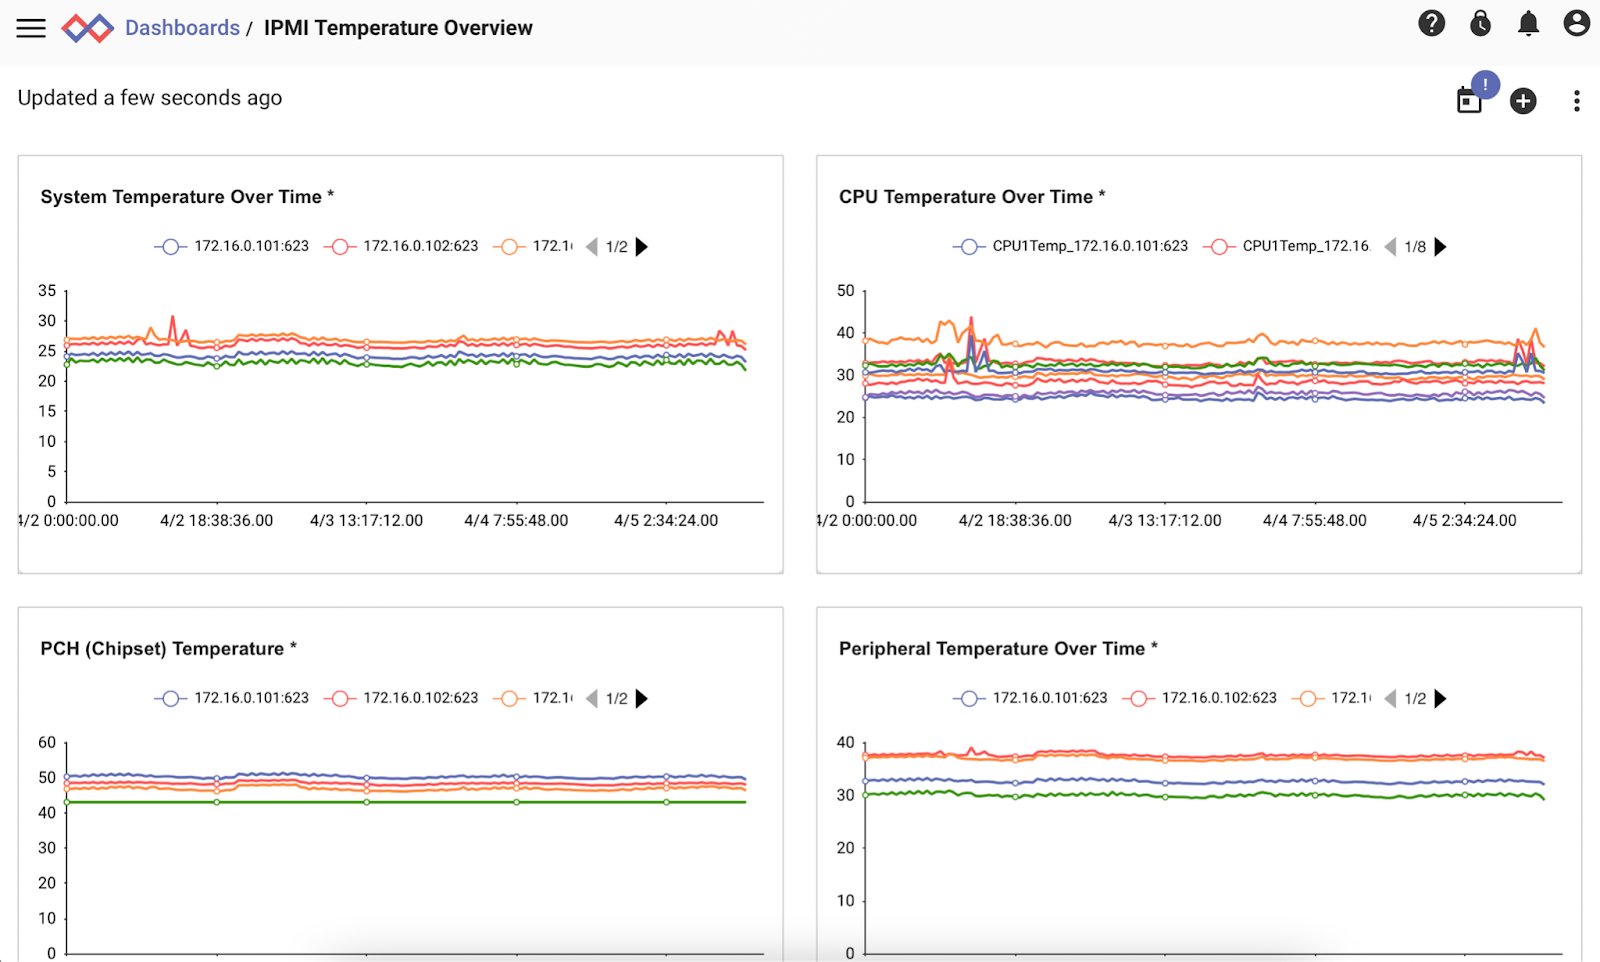
Monitor Daily Temperature Swings
IPMI and Gravwell Part 2: Making an IPMI Kit
DOCUMENTATION
All Gravwell documentation is open to everyone.
If you’re just starting out with Gravwell, we recommend reading the Quick Start first, then moving on to the Search pipeline documentation to learn more.